Static egress for an approved transactional email relay
Evaluate static egress for an approved corporate email relay by verifying authenticated submission, the remote port and written scope.
Separate mail delivery from the network route
A billing service may send receipts through a corporate relay that accepts authenticated connections only from approved addresses. A static egress service can help satisfy an address requirement if its product permits the named connection. The relay still owns mail submission, authentication and delivery policy. Buying an IP address alone does not create permission to send mail or establish delivery quality.
Collect the details from the relay administrator
Ask which submission method, TLS configuration, destination and source addresses the relay accepts. Record who can approve changes and which environment is reserved for testing. A gateway listening port is distinct from the port the relay expects. Consult the specific product's written destination policy for this use, since general protocol support leaves that question open.
If the relay administrator prefers an authenticated HTTPS delivery interface for the workload, compare that option on its own requirements. The application owner can then choose an approved transport suited to the service contract. RFC 8314 on encrypted email submission.
Verify a single authorized delivery
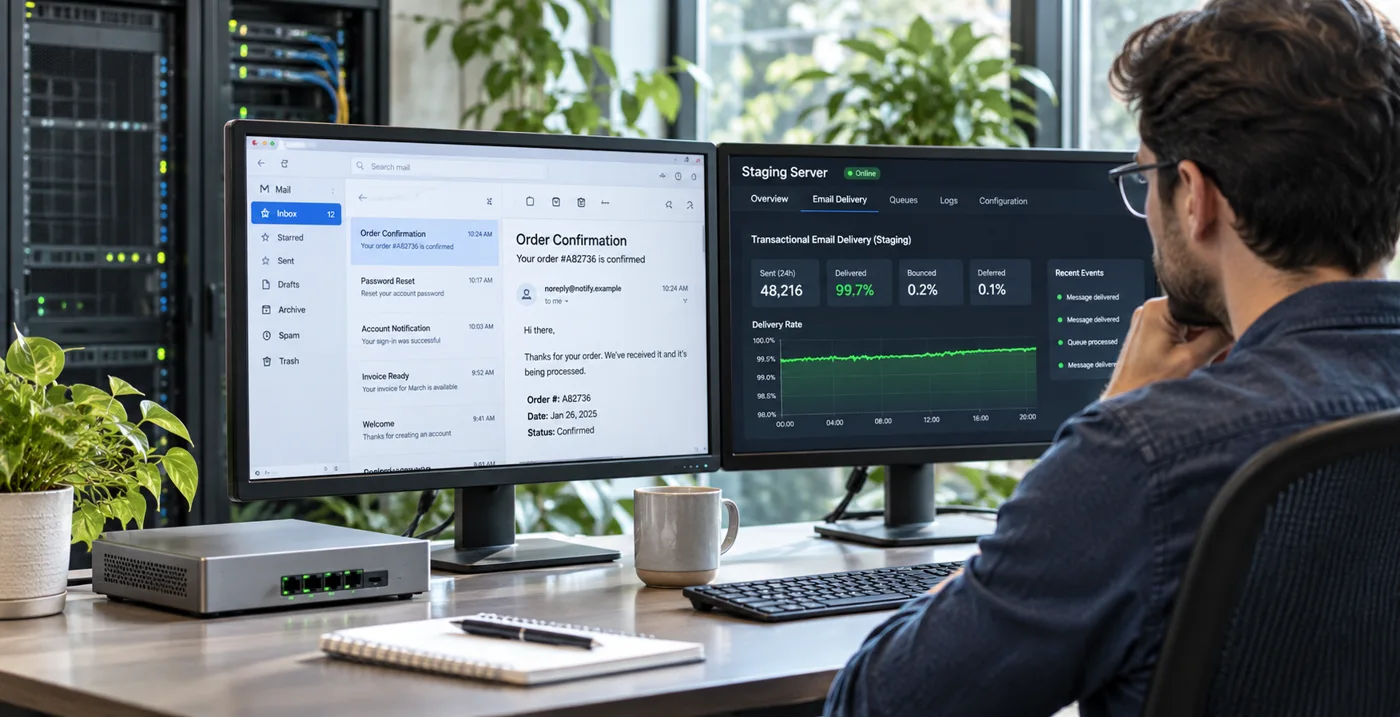
With both providers' approval, send a transactional test message through the corporate account to an approved recipient and check its receipt or relay acceptance in the organization's own logs. If the product does not document the connection, retain the existing approved mail path while obtaining clarification. For XtremeProxy, describe the named relay and request a written compatibility decision before ordering an address. Keep the result with the application's delivery runbook.
An approved relay changes its allowlist window
A billing team uses a corporate transactional relay that recognizes a documented source address. Before renewing the route, obtain the relay owner's accepted submission method, authentication and encryption requirements and the network plan's written compatibility for the named service. Ask the relay operator to observe a single authorized synthetic transaction in its designated test environment. Relay acceptance, final delivery and message handling are different events. Keep the existing approved delivery path available while a new source is being reviewed.
Keep relay submission distinct from inbox placement
A corporate relay can accept an authorized message and later record an independent delivery outcome. Agree with the messaging owner on the exact checkpoint and approved test recipient. Match the network provider's written policy to the named service. A registered port number does not supply permission or a mail service contract.
Define which evidence closes a delivery test. A relay’s acceptance identifier proves handoff to that relay, while a message recorded in a designated test inbox confirms a later stage. Retain the synthetic test identifier across both records so queue delays do not get reported as connection failures.
Separate a network acceptance check from a delivery receipt
With both service owners' approval, a designated test message reaches the relay and receives its own transaction reference. The application can use the relay's authorized record to verify submission. A later delivery receipt, if the arrangement provides one, answers a further question. Write down which event the integration requires before evaluating whether the test passed.
A monthly average can conceal a concentrated invoicing run. The application may submit most of its approved transactional messages during one hour on the last business day. Compare that business schedule with the corporate relay’s documented submission policy and the application’s supported queuing behavior. Work through the expected queue on paper or in the designated sandbox. A stable source assignment can satisfy the network condition while a queueing or capacity constraint still prevents the notification service from meeting its deadline.
A relay may recognize a certificate or account as well as the network source. During a planned change of static egress, hold the approved submission identity and test recipient constant. If the authorized submission works on the old route but fails on the new one, the relay administrator has a narrower difference to investigate. If both routes fail, investigate the shared account, certificate or relay configuration before purchasing another address. The readout should name the stage at which the two observed paths diverged.
Related fieldwork
A transactional relay project needs agreement from both the mail operator and the network provider on the supported connection. Keep the test recipient, permitted environment and expected evidence in the approved runbook. Partner inventory feed allowlists illustrates the related network requirement of a named fixed source. Building an IP allowlist for a partner API integration follows that source through partner approval and replacement. Technical references include RFC 8446, TLS 1.3, IANA service name and port number registry. Review XtremeProxy plans and allowances.
Frequently asked questions
Does a fixed source address guarantee receipt of a transactional message?
No. It can satisfy one network access condition if both services permit it. The relay controls submission policy, and downstream systems influence delivery. Use the relay's own authorized records to distinguish acceptance from receipt.