Proxy authentication for teams with changing office IPs
Choose proxy authentication for distributed teams by matching access rules and credential rotation to the places the client runs.
Start with where the client runs
A workstation behind a stable office connection can be a good candidate for an IP-based access rule. A distributed build system or a remote employee may leave the network through changing addresses. In that case, a credential-based proxy configuration may be easier to manage, subject to the client and product supporting the same method.
Work through the change calendar
List the people who can update an access rule, the systems that need connectivity and the evidence required for approval. If a build service changes egress during a scheduled deployment, the on-call engineer should know which authorized path the job expects. For credential-based access, give each logical application its own secret where the available plan allows. Use your team's normal access controls and rotation process.
Consider the person who approves changes outside office hours. If the only administrator is unavailable during a routine network migration, an otherwise suitable access method can still delay the release or the following day's report. RFC 1928, SOCKS protocol version 5.
Measure operational fit
Run a normal test from each approved environment and then rehearse a routine credential renewal or access-list change. Measure how long the team takes to restore its own fixture. Ask XtremeProxy which authentication choices apply to your software, how changes become effective and whether separate application credentials are available. These answers tell the operations team what a future office move or deployment change will cost.
A developer's home address changes after an ISP renewal
A distributed team has a stable outbound service for scheduled jobs and changing home networks for developers. Identify which actor needs access to which project. A fixed allowlist entry may suit the job runner. A provider-supported credential flow may suit individual authorized users when managed under the team's policy. Test source recognition from the scheduled environment and retire unused access when the developer changes roles. Keep secret values out of the access record.
Separate source trust from user identity
An allowlisted office address may authorize many users behind one shared connection. The application may still need individual authentication or distinct workload credentials. Document the team's joiner and leaver process and who can approve a replacement source. Validate the actual scheduled environment when home users have different network conditions.
A corporate office can have several outward routes. Traffic from a CI runner may leave through another address even when a developer reaches it through the same corporate network. Have the gateway administrator identify the observed runner source during an agreed test before expanding an allowlist.
Rehearse offboarding with a synthetic identity
An access owner retires one test identity while leaving the scheduled reporting job active. Verify that the retired identity loses the documented capability and that the runner still retrieves its approved fixture. If both stop working, their access depended on a shared control. Record that dependency before applying the same change to a real team member.
A team sometimes places both office staff and an automated job behind the same egress. If the gateway accepts that source address, it may be unable to distinguish the employee’s test from the scheduled job for billing or audit purposes. Decide who needs individual attribution and which supported client identity supplies it. An unexpected spike at midnight is easier to investigate when the reporting job has its own assignment and reference, even if the network boundary remained unchanged all month.
Document the relationship between office-network policy and the application's separate login. A team member leaving an approved Wi-Fi network might lose source-based access while their application account remains active. Conversely, disabling the account can revoke application access while the gateway still accepts traffic from the shared office. An offboarding exercise should verify whichever of those layers the organization relies upon. Identify who owns each one so a later contractor change brings both access records to the appropriate reviewer.
Related fieldwork
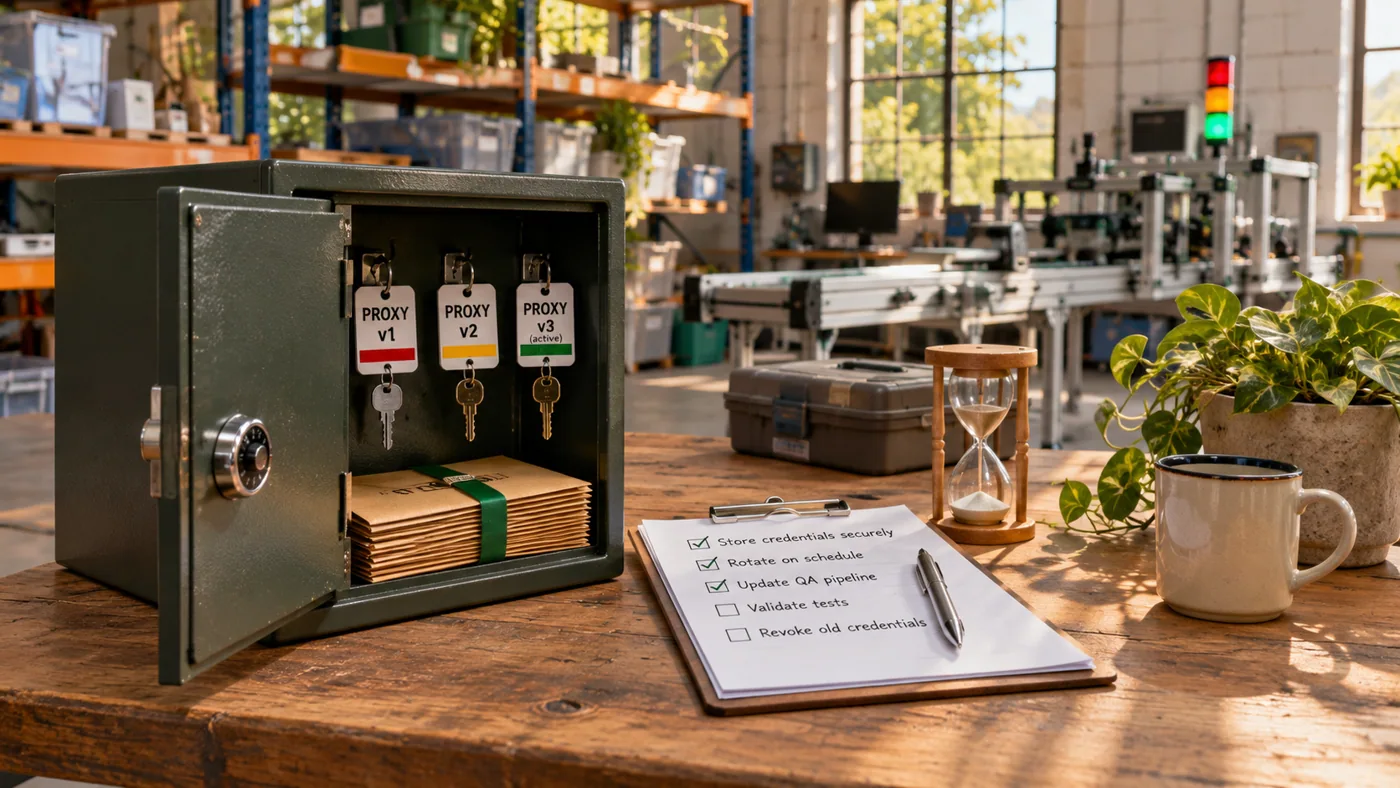
A flexible team setup should make it possible to retire one identity without interrupting an unrelated scheduled job. Confirm this property under the supported access controls before extending the arrangement to contractors. Partner inventory feed allowlists shows a stable partner source rule. How to store and rotate proxy credentials in a QA pipeline explains how to move workloads to a new credential without exposing the secret. Technical references include OWASP secrets management guidance. Review XtremeProxy plans and allowances.
Frequently asked questions
Can a contractor share the production runner's gateway credentials?
Give each authorized workload or user the narrowest access the supported system permits and document the owner. Shared long-lived credentials make revocation and attribution difficult. Review contractor access separately when the engagement ends.