Proxy listening ports and destination ports explained
Distinguish a proxy listening port from a destination port and document both sides of a business application connection.
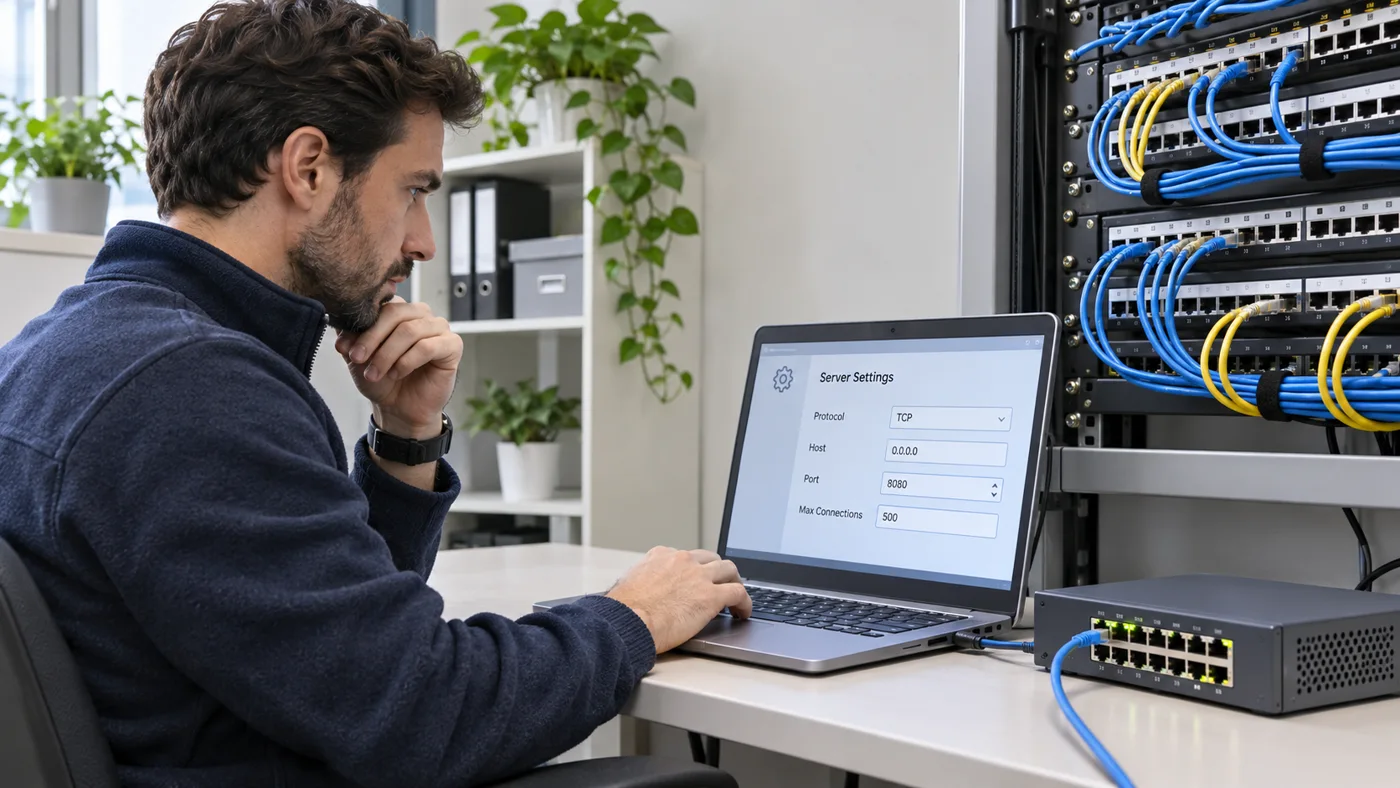
One connection can involve two port numbers
A supplier may give your application a gateway hostname and port where the proxy accepts clients. The application then asks to reach a separate host and destination port. Seeing a number in the gateway configuration establishes where the application should connect. It does not establish which services the proxy will let the application contact on the far side.
Read a configuration as a pair
Consider a reporting app that connects to a company-owned HTTPS API. Its network diagram should show a client-to-gateway segment and a gateway-to-API segment. Record the transport and port on each segment. An entry in the IANA service registry describes an assignment or convention. Actual access on a chosen proxy plan depends on the product policy and destination approval.
An application's error message may mention only one of the two ports. Note whether it failed to reach the gateway or whether the gateway rejected the requested service, and include that distinction in the handoff. IANA service name and port number registry.
Keep a reproducible support record
If the app cannot reach the approved endpoint, give support the time, gateway region, intended service, expected result and an anonymized order reference. Keep secrets and customer payloads out of the report. Ask XtremeProxy for documented permission for the named service and transport before reserving an address. This avoids buying a suitable geographic location with an incompatible outbound policy.
Port 8080 on the gateway and 443 on the destination
A fulfillment record lists an HTTP-aware gateway listening on 8080. The team's approved application connects through it to an HTTPS service on 443. Keep two distinct fields in the integration record and have the destination owner confirm the approved service. If a second service has different destination requirements, consult the relevant plan policy before scheduling it. A successful connection to the gateway listener alone supplies no evidence that a different destination or transport is allowed.
Document the destination as a service
A number alone omits the destination identity, transport and authorization. Record the named partner service and its documented connection requirement beside the provider's permitted destination policy. The gateway listener, the remote port and the application's own authentication all have independent roles in the integration.
A destination URL that omits its port still has an effective port. Write that implied port into the approved connection diagram beside the explicitly configured gateway port. This makes support tickets comparable when one client prints the full destination authority and another logs only its bare hostname.
Compare an approved service change with a network change
A partner moves its staging application to a new supported endpoint. Update the named destination and documented policy in the test record, retaining the original gateway assignment. Check the application's expected response marker and partner observation. A failure after the move may concern the new destination's configuration rather than the unchanged gateway listener.
Consider a migration where the authorized HTTPS service moves behind a new load balancer while retaining its existing hostname and destination port. An engineer who records only “443 is permitted” cannot tell support which named service was expected after the move. Include the target service owner and the approved hostname with its port, then compare the fixture’s returned identifier before and after the migration. One familiar port number can serve many unrelated tenants and does not identify the application that actually responded.
Include the environment in every destination approval. A partner may permit a staging hostname for a defined integration exercise while its live service has a separate application policy. Two endpoints using the same destination port can therefore have different authorization and expected results. Use the order details to identify how the client reaches the gateway and the partner's service record to identify where the application goes next. The acceptance evidence should connect those two named facts to one approved response from the intended environment.
Related fieldwork
Before ordering a specialized path, keep the gateway listener, approved destination service and destination transport in separate fields. A received application response completes the practical check for that service. Partner inventory feed allowlists applies the same discipline to a named partner integration. Does a SOCKS5 proxy support UDP for your application? explains why a second transport requires evidence of its own. Technical references include RFC 9110, HTTP semantics. Check XtremeProxy location coverage.
Frequently asked questions
Can the IANA service registry establish that a particular plan permits a port?
The registry documents assigned service names and ports. The provider and destination owner establish the applicable permission and product behavior. Retain their documented decision beside the application's required connection.