Forward proxies and reverse proxies in an application diagram
Read an application network diagram and identify where an outbound forward proxy or an inbound reverse proxy belongs.
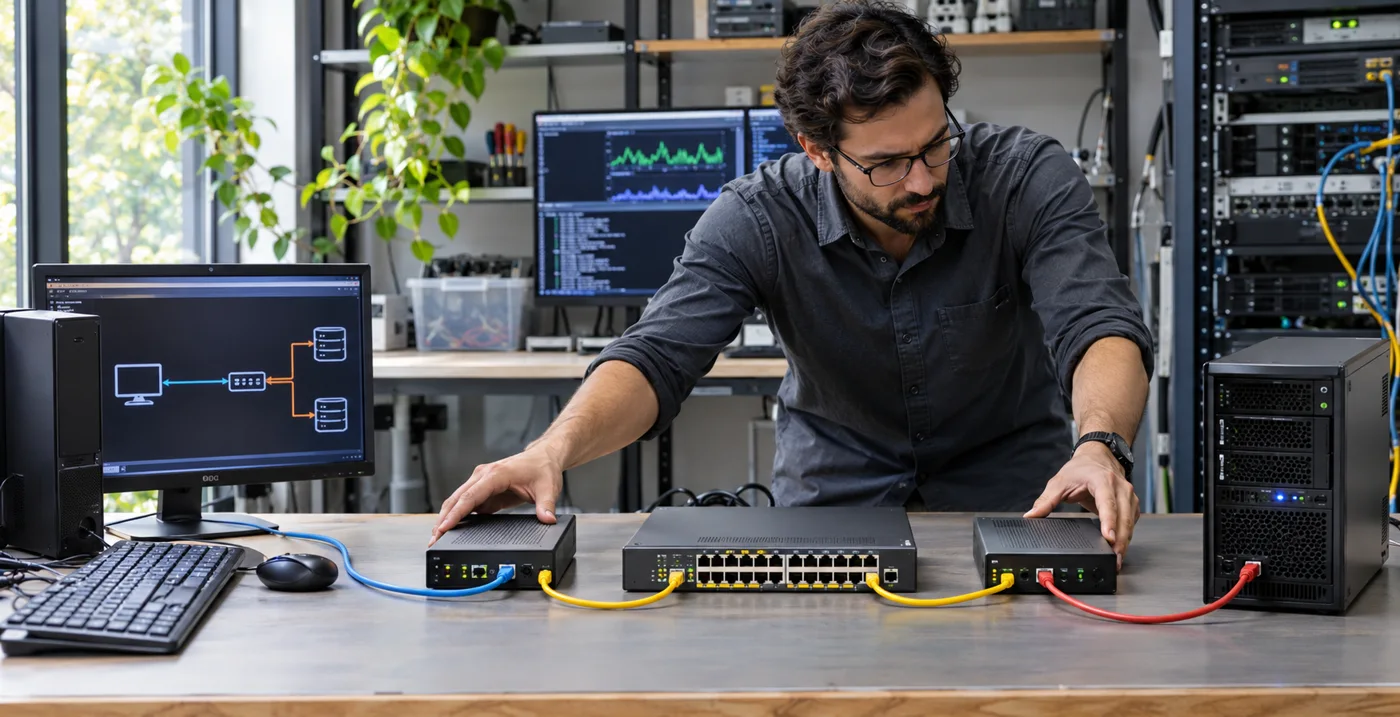
Find the client that initiates the request
A forward proxy acts on behalf of a client making an outbound request. A reverse proxy acts in front of an origin service that receives incoming requests. A company can use both in the same transaction. For example, a QA runner uses approved egress to reach a company's website, and the website sits behind an inbound gateway that chooses an application server.
Identify the component your team controls
If the problem is delivering users to healthy backend servers, examine the inbound delivery layer. If a cloud job needs to appear from a pre-approved IP to a business partner, examine outbound egress. Draw the sequence of components and mark where source addresses, certificate checks and access rules are evaluated. The person operating one side may have little visibility into the other.
During a handoff, put the party responsible for each gateway next to it on the diagram. An outbound application engineer and a website edge operator may both say proxy while referring to different components. MDN guide to proxy servers and tunneling.
Order the service that fixes the problem
For XtremeProxy, describe who originates the connection, which destination you control or have permission to access and what observation should change. A short diagram can reveal that a request for a proxy actually involves two separate teams and contracts. It also gives support a shared picture when an origin log records a different address from the one an engineer expected to find.
Two gateways appear in the same partner integration
A reporting worker uses an outbound gateway to reach a partner's public API. The partner places its own inbound gateway in front of the application servers. Draw the worker, outbound service, partner edge and application as separate nodes. Label who authenticates the client at each relevant step and which component can observe a specific request reference. A first-party permission error returned by the partner application needs a different owner from a failure connecting to the outbound gateway.
Name the observer at each boundary
An origin may log its immediate reverse proxy while the application also receives a trusted forwarded value under its own infrastructure policy. Keep the recorded field and its trusted source explicit. Outbound and inbound operators can share a correlation ID on an approved integration without seeing identical network events.
A tracing identifier is useful only where both participants have agreed to propagate it. An inbound gateway may issue its own reference rather than forward the caller’s. For an owned test, record the mapping at that boundary so a missing identifier in downstream logs is interpreted correctly.
Make the handoff testable without sharing secrets
Give a synthetic request an opaque reference that both approved operators can correlate. The outbound team records the selected assignment and the partner checks its own inbound and application logs. A gap between two known observations directs the next question to the appropriate operator. Neither party needs to send its private infrastructure diagram or reusable credentials.
A reverse proxy can serve an approved cached response without contacting its application server during that request. The absence of an origin log entry therefore does not automatically show that an outbound proxy failed to reach the partner. Compare the partner edge’s request reference and cache status with the final response marker. A diagram that includes the cache boundary gives both teams a plausible explanation for how the customer received a response while the application server recorded no matching event.
A client-visible address in an application log may have been added or transformed by trusted infrastructure. Label it with the component that produced it and its documented meaning. The partner edge’s actual network peer and an application-level field describing an earlier hop can both be useful, but comparing them as if they were the same observation creates a false discrepancy. A simple diagram with separate arrows for observed peers and forwarded metadata gives support a useful map for interpreting a particular trace.
Related fieldwork
Identify the owner who can verify each transition through the route. A diagram is most useful when a real synthetic request can be traced through the components it depicts. Partner inventory feed allowlists gives an example in which the partner's observed source matters. Proxy or VPN for a regional application test? helps choose the scope of regional routing for the originating application. Technical references include RFC 9110, HTTP semantics. Review XtremeProxy plans and allowances.
Frequently asked questions
Can a reverse proxy replace a customer's fixed egress requirement?
It serves a different part of the path. A partner evaluating the source of incoming requests needs evidence about the source visible at its boundary. Document that requirement separately from how the partner routes accepted requests internally.